Important
All writeups will be password-protected using the challenge flag, in accordance with HTB’s Terms of Service.
With a few mobile-related projects coming up, I’ve decided to dust off my skills and warm up with some Hack The Box (HTB) mobile challenges.
Mobile reverse engineering and pentesting get rusty fast if you don’t practice, so I’m using HTB as a low-stakes playground to get back into the groove.
Whenever I stumble upon something interesting along the way, I’ll drop a few casual notes in this blog site also:
- Random Field Notes: Quick thoughts or interesting tricks I encounter while picking apart apps (root/jailbreak checks, crypto slip-ups, or odd logic flows).
- Tooling & Handy Scripts: Tools that make life easier (Frida snippets, Objection, Jadx, Ghidra, etc.) whenever they prove useful.
- Mini Cheat Sheets: Small setups and reminders I write for myself so I don’t forget them later.
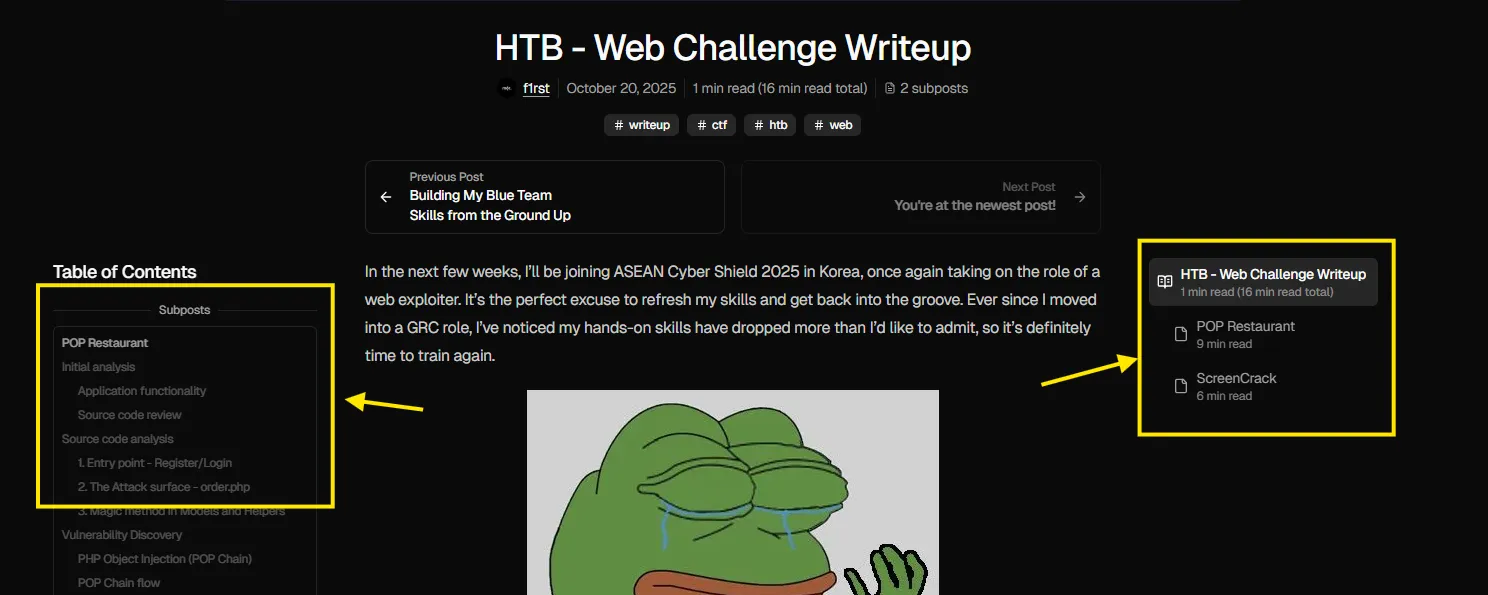
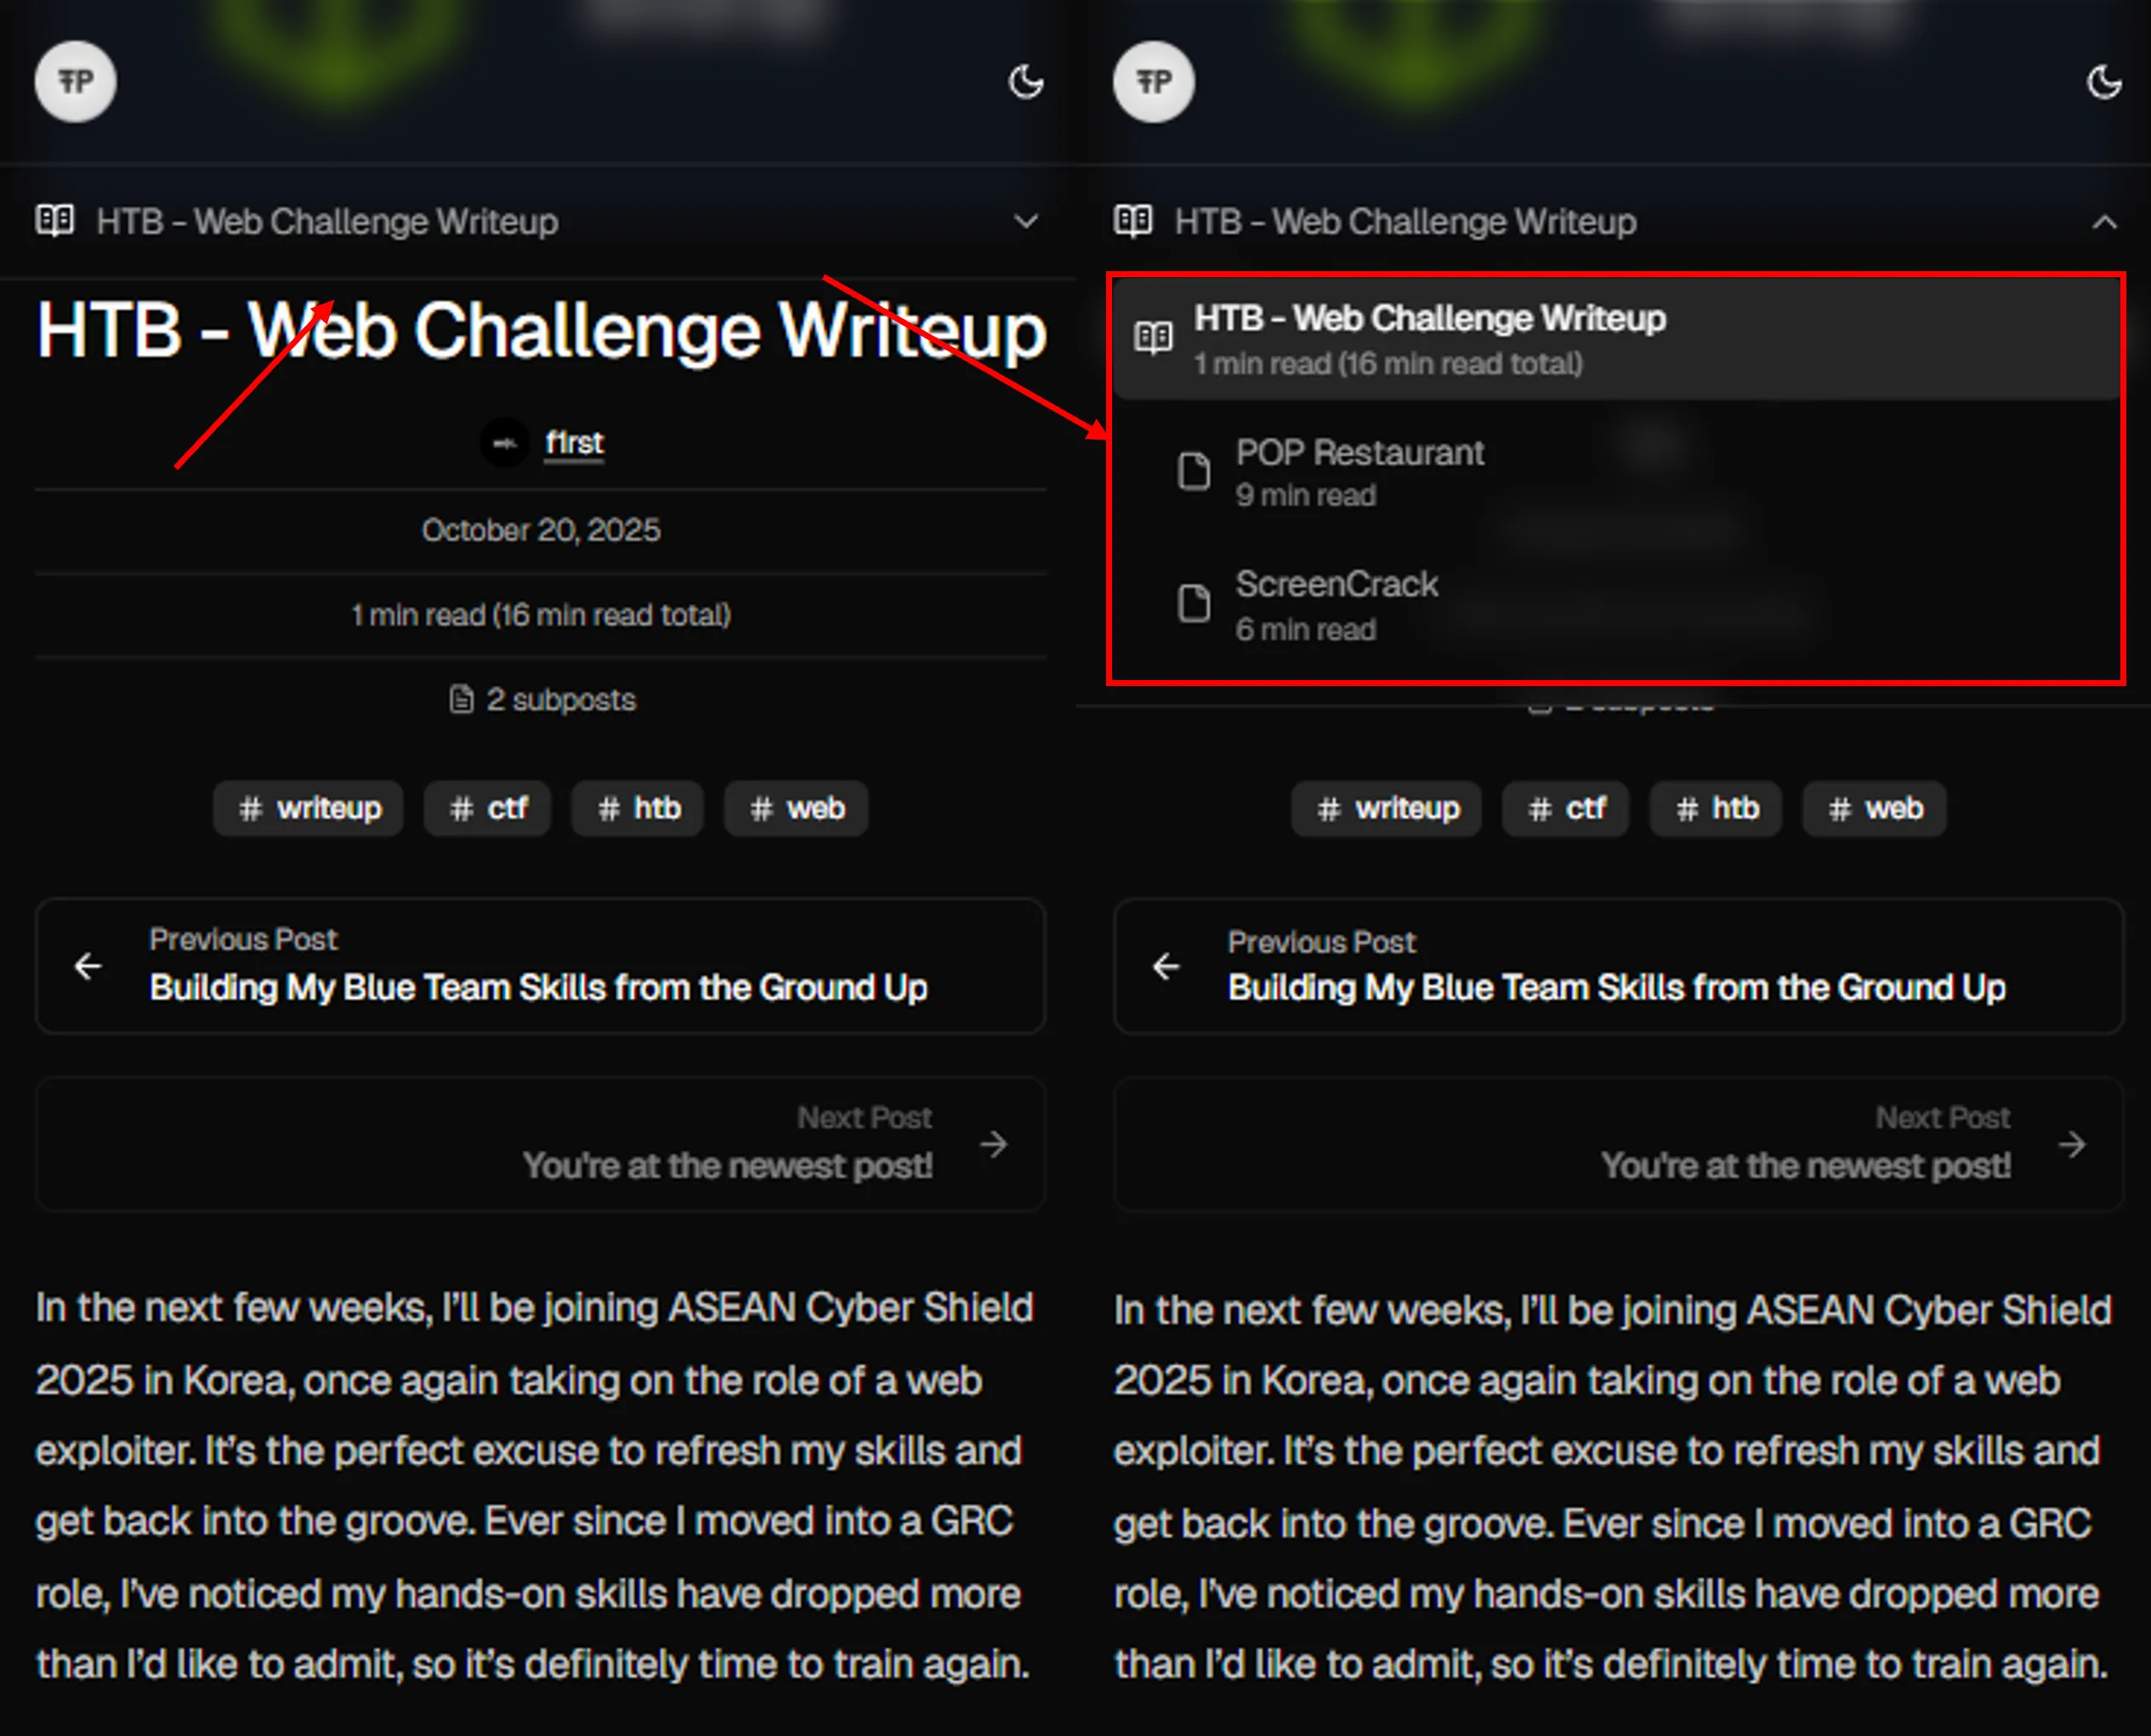
You can check out the sub-post on the side if you’re on desktop, or in the mobile navigation bar if you’re on your phone, for detailed writeups of each challenge.